WordPress Security
A hacked WordPress site can cost you trust, search rankings, and—in the worst-case scenario—customer data. We’ll secure your installation before it comes to that.

WordPress Security Agency
WordPress security encompasses all measures that protect your website from attacks, malware, and data loss. From login protection to regular updates to firewall configuration: We secure every level of your installation.
Build protection instead of
limiting damage
Security audit with
a specific action plan
Emergency Assistance for
Hacked Websites
Why WordPress Websites Are Targeted
WordPress powers over 40 percent of all websites worldwide. This makes it the most attractive target for automated attacks. Brute-force attacks on the login, vulnerabilities in outdated plugins, and insecure file permissions are the most common entry points. Most attacks are automated and target websites that no one has specifically singled out. That’s why even a company website with 200 visitors a month can be affected. Anyone who thinks they’re too small to be targeted is confusing attention with vulnerability.
Security is a state of being, not a project
A one-time security setup isn’t enough. New vulnerabilities are discovered every day, plugins release security updates, and attack methods continue to evolve. What’s secure today could be an open door in three months. That’s why we continuously monitor your website, apply updates promptly, and respond before a security alert turns into an incident. Security and maintenance go hand in hand.
WordPress security consists of several layers that must work together—from access protection to server configuration to a contingency plan. Here's a look at what this protection entails.
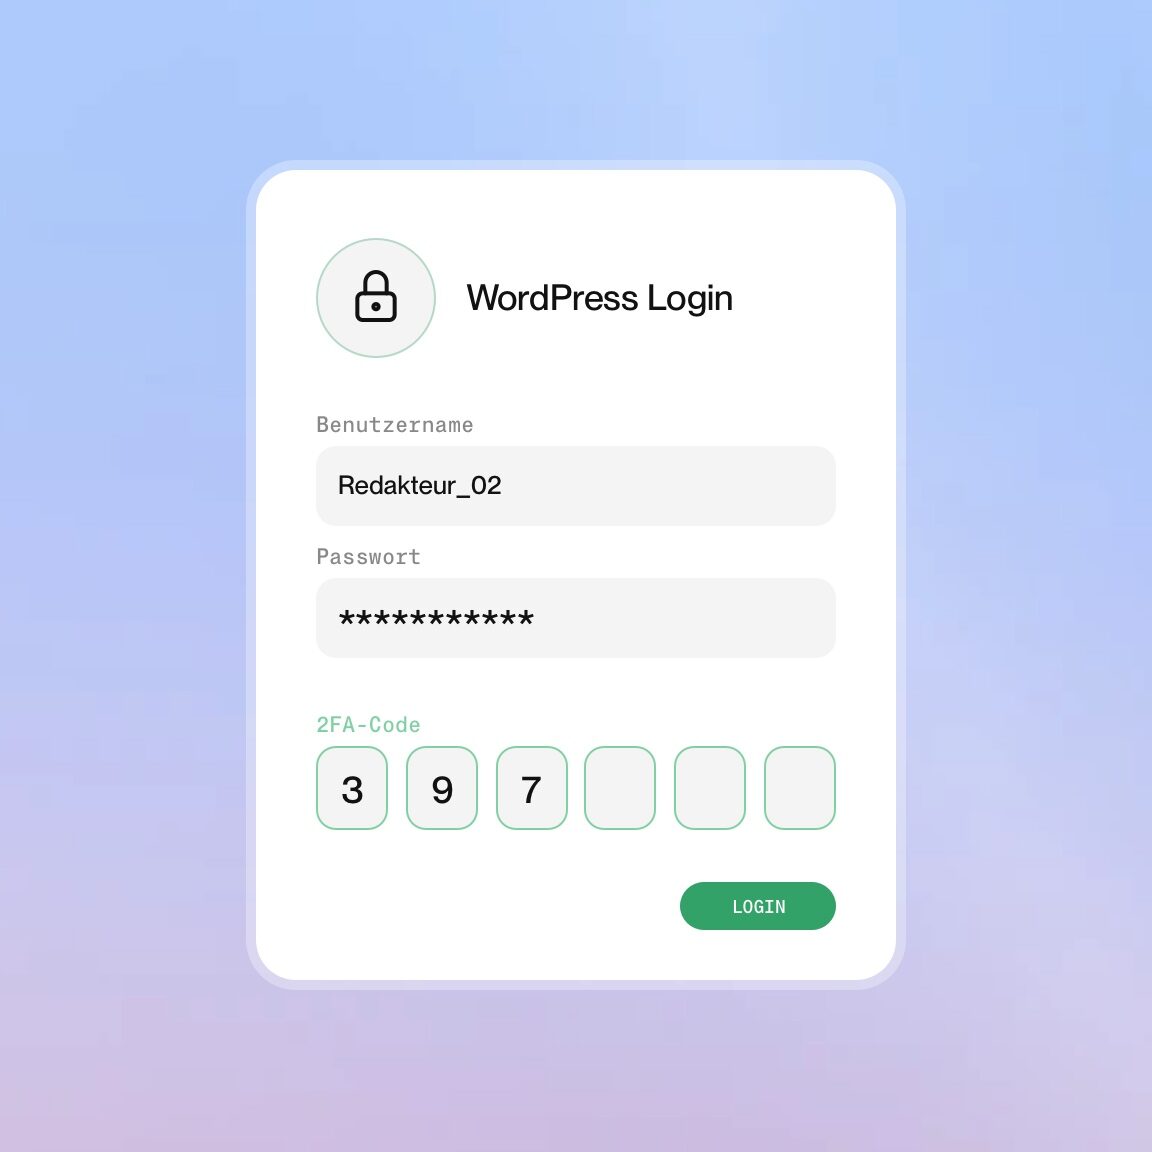
Login Protection
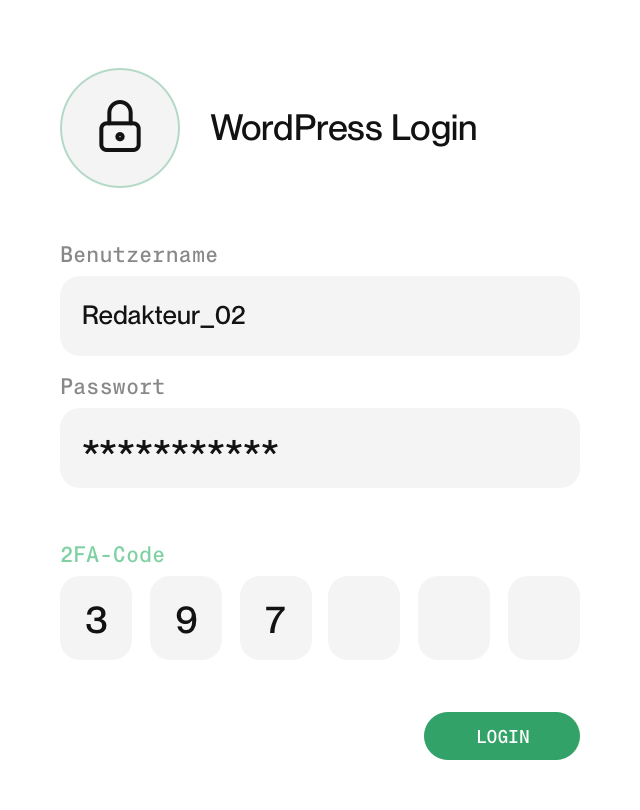
The login is the most common target of attacks. We secure it with two-factor authentication, password policies, and login limits. Brute-force attacks are automatically blocked, and the login URL is moved so that automated scanners can no longer find it.
Firewall and WAF
A web application firewall filters out malicious traffic before it reaches your website. We configure rules that block known attack patterns and detect suspicious activity. The rule sets are continuously updated to ensure that new waves of attacks are also intercepted.
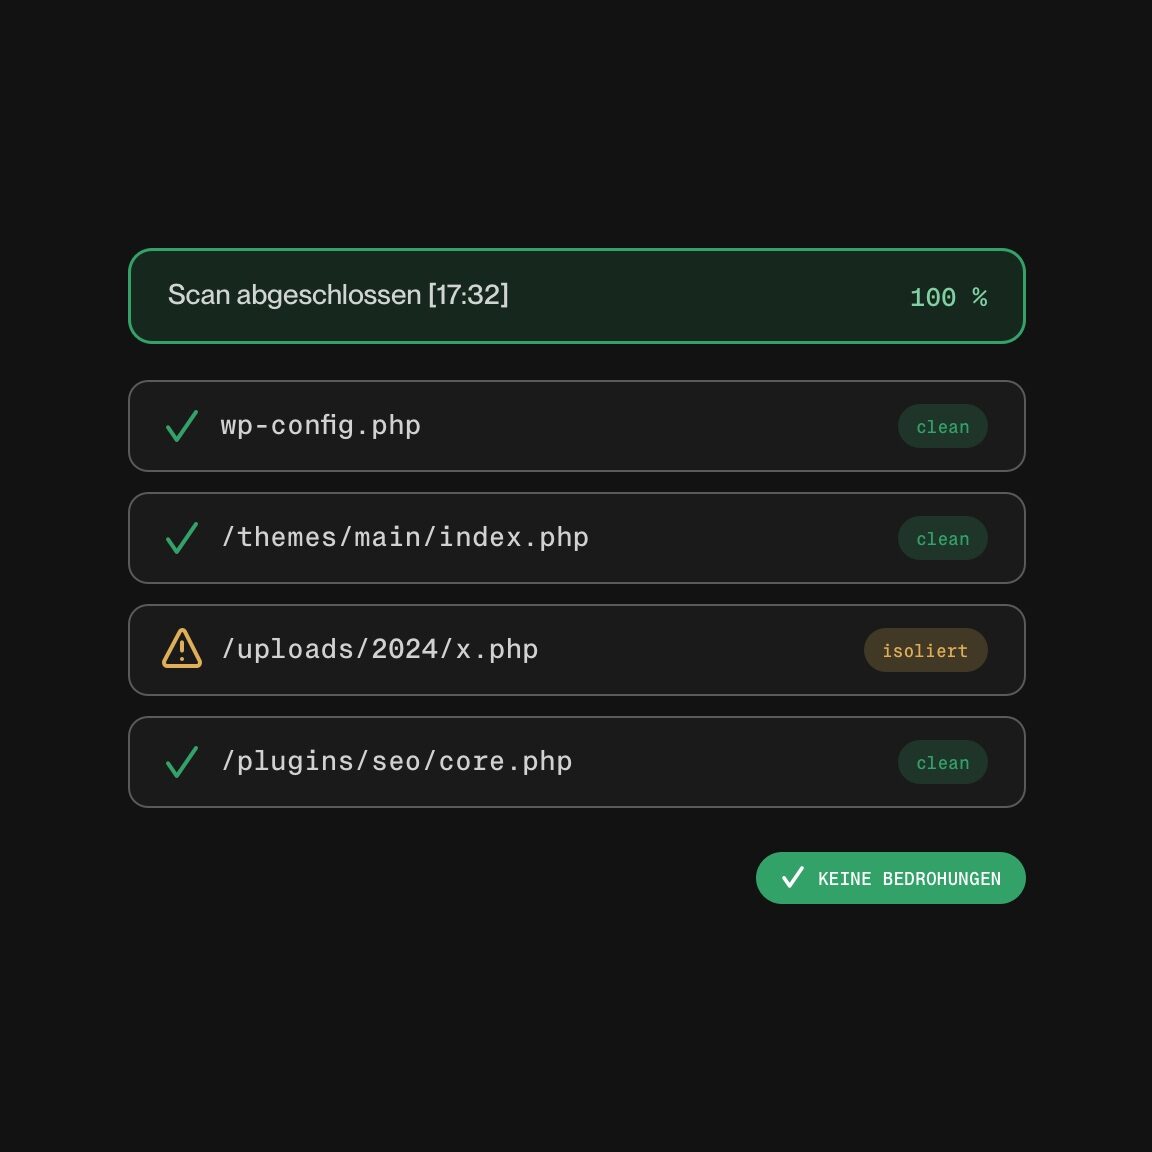
Malware Scan
Regular scans check your WordPress files for changes, injected code, and known malware signatures. Infected files are isolated and cleaned up. File integrity monitoring also detects hidden backdoors that would otherwise reactivate after a cleanup.
Update Management
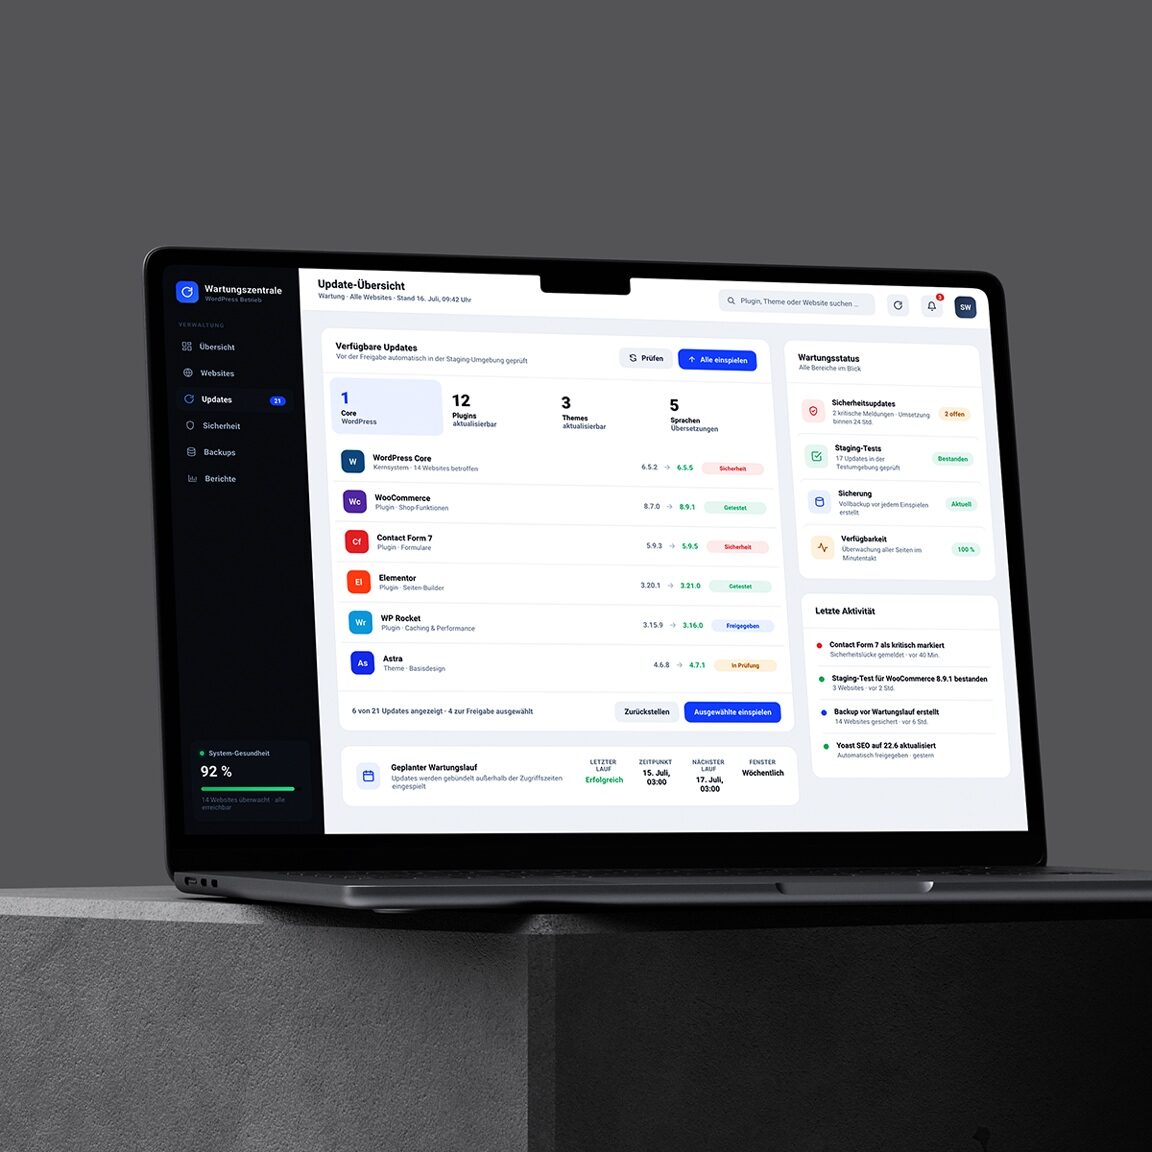
Outdated plugins and themes are the biggest security risk in WordPress. We keep the core, plugins, and themes up to date and test updates in a staging environment first. We install critical security updates within 24 hours.
Backup Strategy
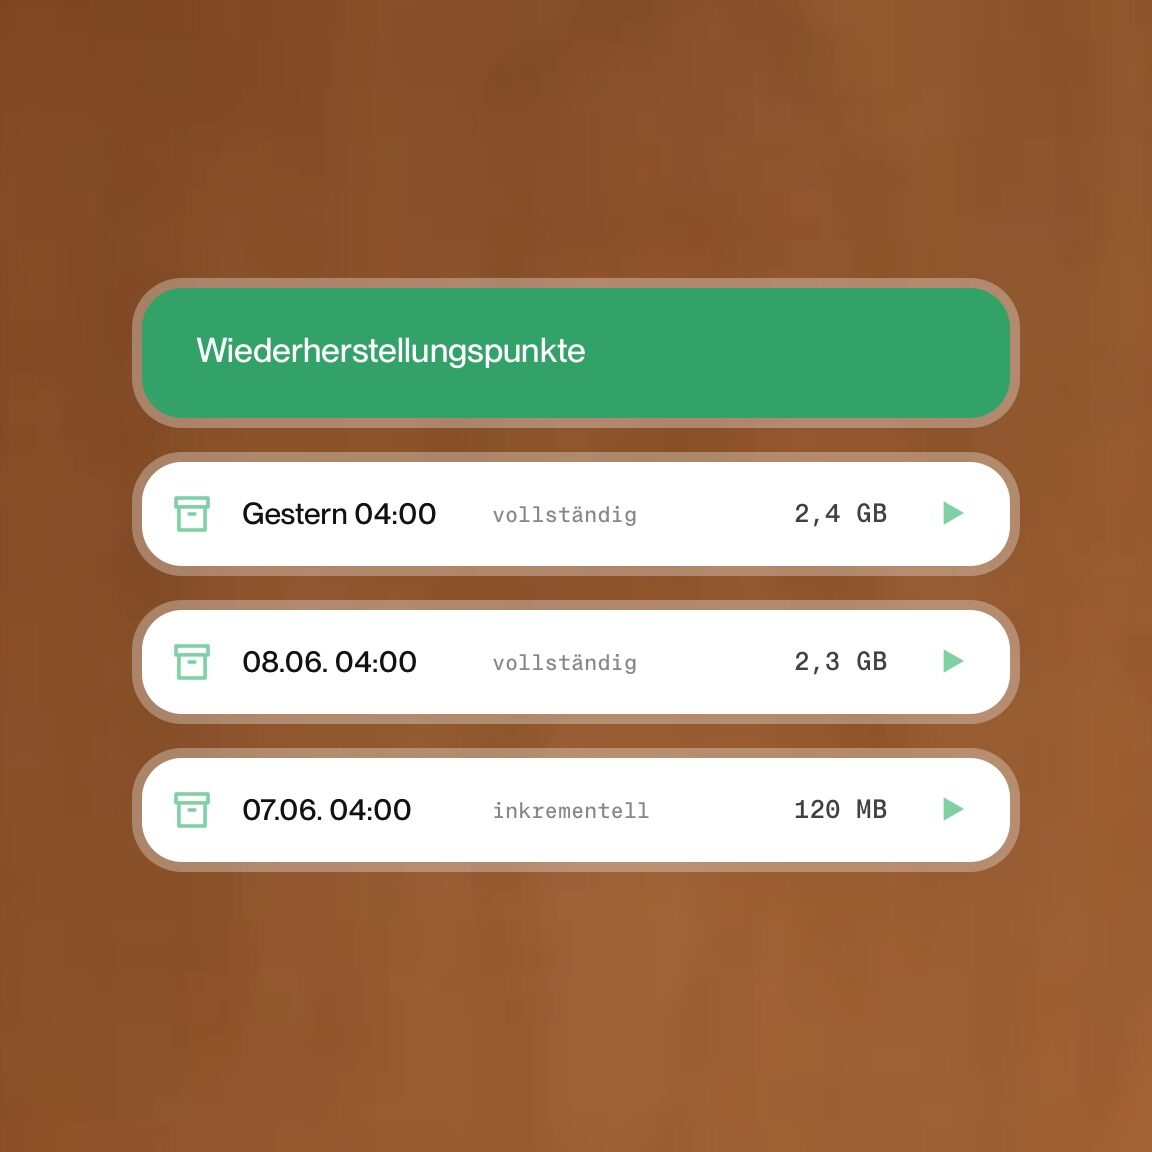
Backups are the last line of defense. We set up daily automatic backups, store them off-site, and test the restore process regularly. A backup that has never been restored is not a backup—it’s an assumption.

Emergency Response
When a website has been hacked, every hour counts. We analyze the attack, isolate the affected areas, remove the malware, and restore the site from clean backups. Then we patch the vulnerability that made the attack possible in the first place.
These companies know how we work


A security audit identifies vulnerabilities before attackers find them. We systematically check your WordPress installation: core version, plugin versions, theme security, file permissions, database configuration, and server settings. Each vulnerability is assessed based on risk and effort. The result is a prioritized action plan that addresses the most critical vulnerabilities first. We also check whether your website has already been compromised: hidden backdoors, injected code, and unknown admin accounts are identified. For websites that process personal data, we expand the audit to include data protection aspects. We deliver the results to your team fully documented, including recommendations for action. This gives you a solid foundation, even if you handle the implementation yourself. A WordPress security agency performs these checks regularly, not just once.
„seitenweise impressed us with fast delivery, friendly communication, and their patience in incorporating our requests! If you want a fast, attractive, and SEO-optimized WordPress website, you should have one built here.“

Michael Bykovski
Computerra
„What particularly impresses us about Seitenweise is not only its technical expertise, but also its proactive approach.“

Dirk Bockelmann
DFT
„To me, having a strong partner is important. Someone who is “passionate” about their work, who offers well-reasoned professional objections but also accepts and continues to fully support my decisions as a client when I choose a different path. I’ve been working very successfully with seitenweise in this way for many years—both in day-to-day operations and on many large-scale projects.“

Veal from Martina
Liebich & Partner
„In addition to the entire team’s tremendous expertise, we especially appreciate how easy and quick it is to get in touch with them, even when things get urgent. Every problem, no matter how small, is taken seriously and resolved immediately.“

Julian Ellermann
arcus physio
„seitenweise impressed us with fast delivery, friendly communication, and their patience in incorporating our requests! If you want a fast, attractive, and SEO-optimized WordPress website, you should have one built here.“
Michael Bykovski
Computerra
„What particularly impresses us about Seitenweise is not only its technical expertise, but also its proactive approach.“
Dirk Bockelmann
DFT
„To me, having a strong partner is important. Someone who is “passionate” about their work, who offers well-reasoned professional objections but also accepts and continues to fully support my decisions as a client when I choose a different path. I’ve been working very successfully with seitenweise in this way for many years—both in day-to-day operations and on many large-scale projects.“
Veal from Martina
Liebich & Partner
„In addition to the entire team’s tremendous expertise, we especially appreciate how easy and quick it is to get in touch with them, even when things get urgent. Every problem, no matter how small, is taken seriously and resolved immediately.“
Julian Ellermann
arcus physio
Projects
STABL
STABL ansehen
Schmidt
Schmidt ansehenFrequently
Asked
Questions
WORDPRESS
SAFE
We'll protect what you've built.
seitenweise is a digital agency based in Bielefeld, founded in 1999. Through more than 500 projects, we’ve gained in-depth experience with WordPress—from development through ongoing operations—including instances where things went wrong. That’s why security isn’t just an add-on for us—it’s an integral part of every installation. Since development and operations are handled by the same team, security measures aren’t added as an afterthought but are built right into the system’s architecture. We also take over existing installations—preferably before a crisis hits.
Marcel and André are your points of contact at seitenweise. They're happy to answer any questions you may have about WordPress security.

Whether it's a security audit, hardening, ongoing monitoring, or immediate assistance after an attack: Tell us where your WordPress website stands. During the initial consultation, we'll let you know which measures should be prioritized.